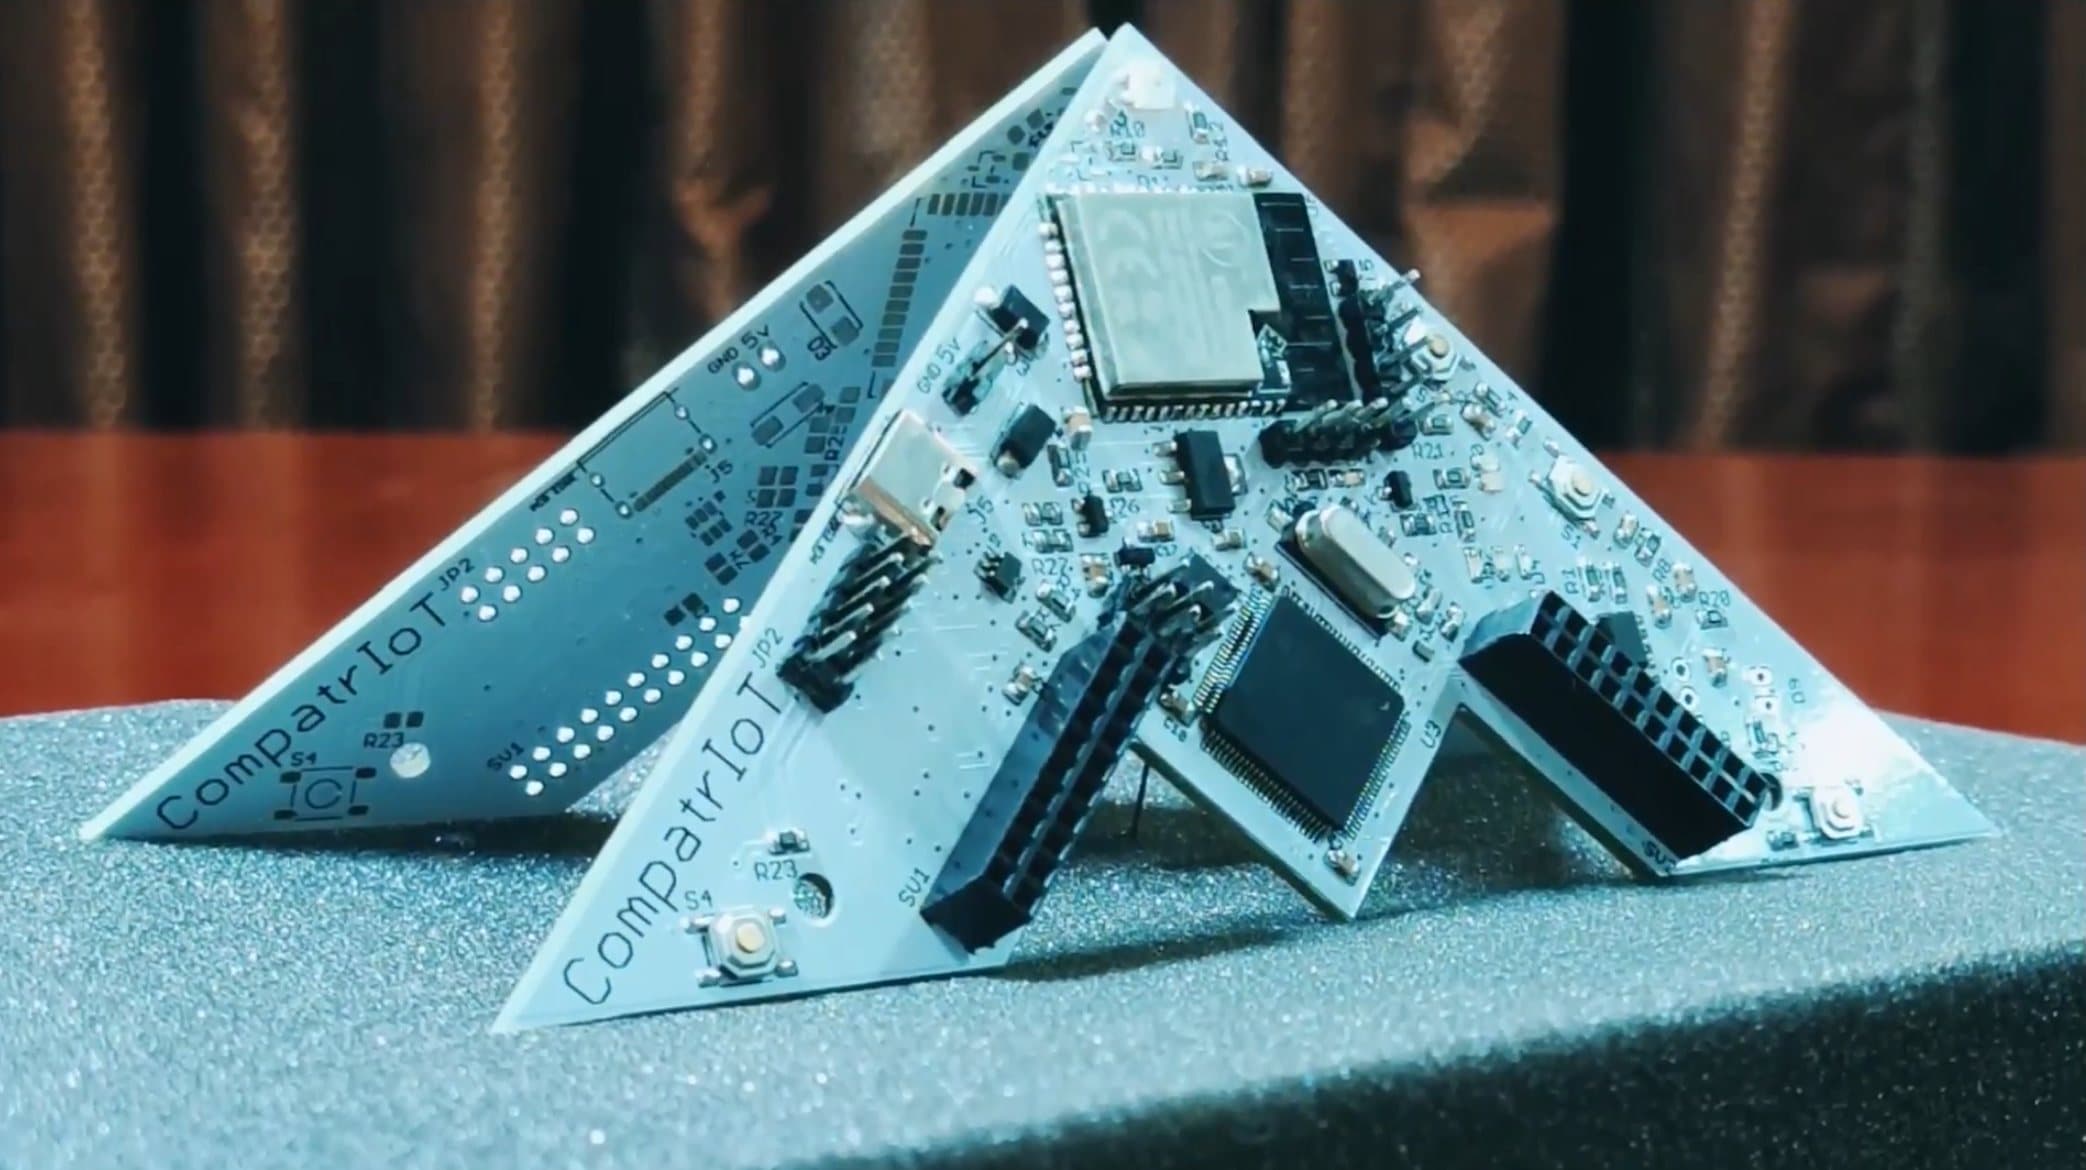
What it is
Most people learn hardware security from slides. CompatrIoT is a physical, open-source training board you attack for real — built for security researchers, hobbyists, and students. Dual microcontrollers (an STM32 and an ESP32) give it broad protocol coverage, and the on-board targets — SPI flash, I2C EEPROM, sensors, programmable LEDs, JTAG/SWD debug ports, and a USB serial console — turn every classic hardware attack into something you can practice hands-on.
The training labs
Twenty gamified labs walk from first contact to full compromise, with progressive difficulty:
- UART — port identification two ways, then talking to the target.
- JTAG/SWD — pinout identification, firmware extraction, firmware patching, and peripheral access.
- I2C — chip reconnaissance, communication sniffing, memory dumping.
- SPI — chip recon, sniffing, and full flash firmware extraction.
- BLE — scanning, GATT enumeration, protocol sniffing, device control, and LTK cracking.
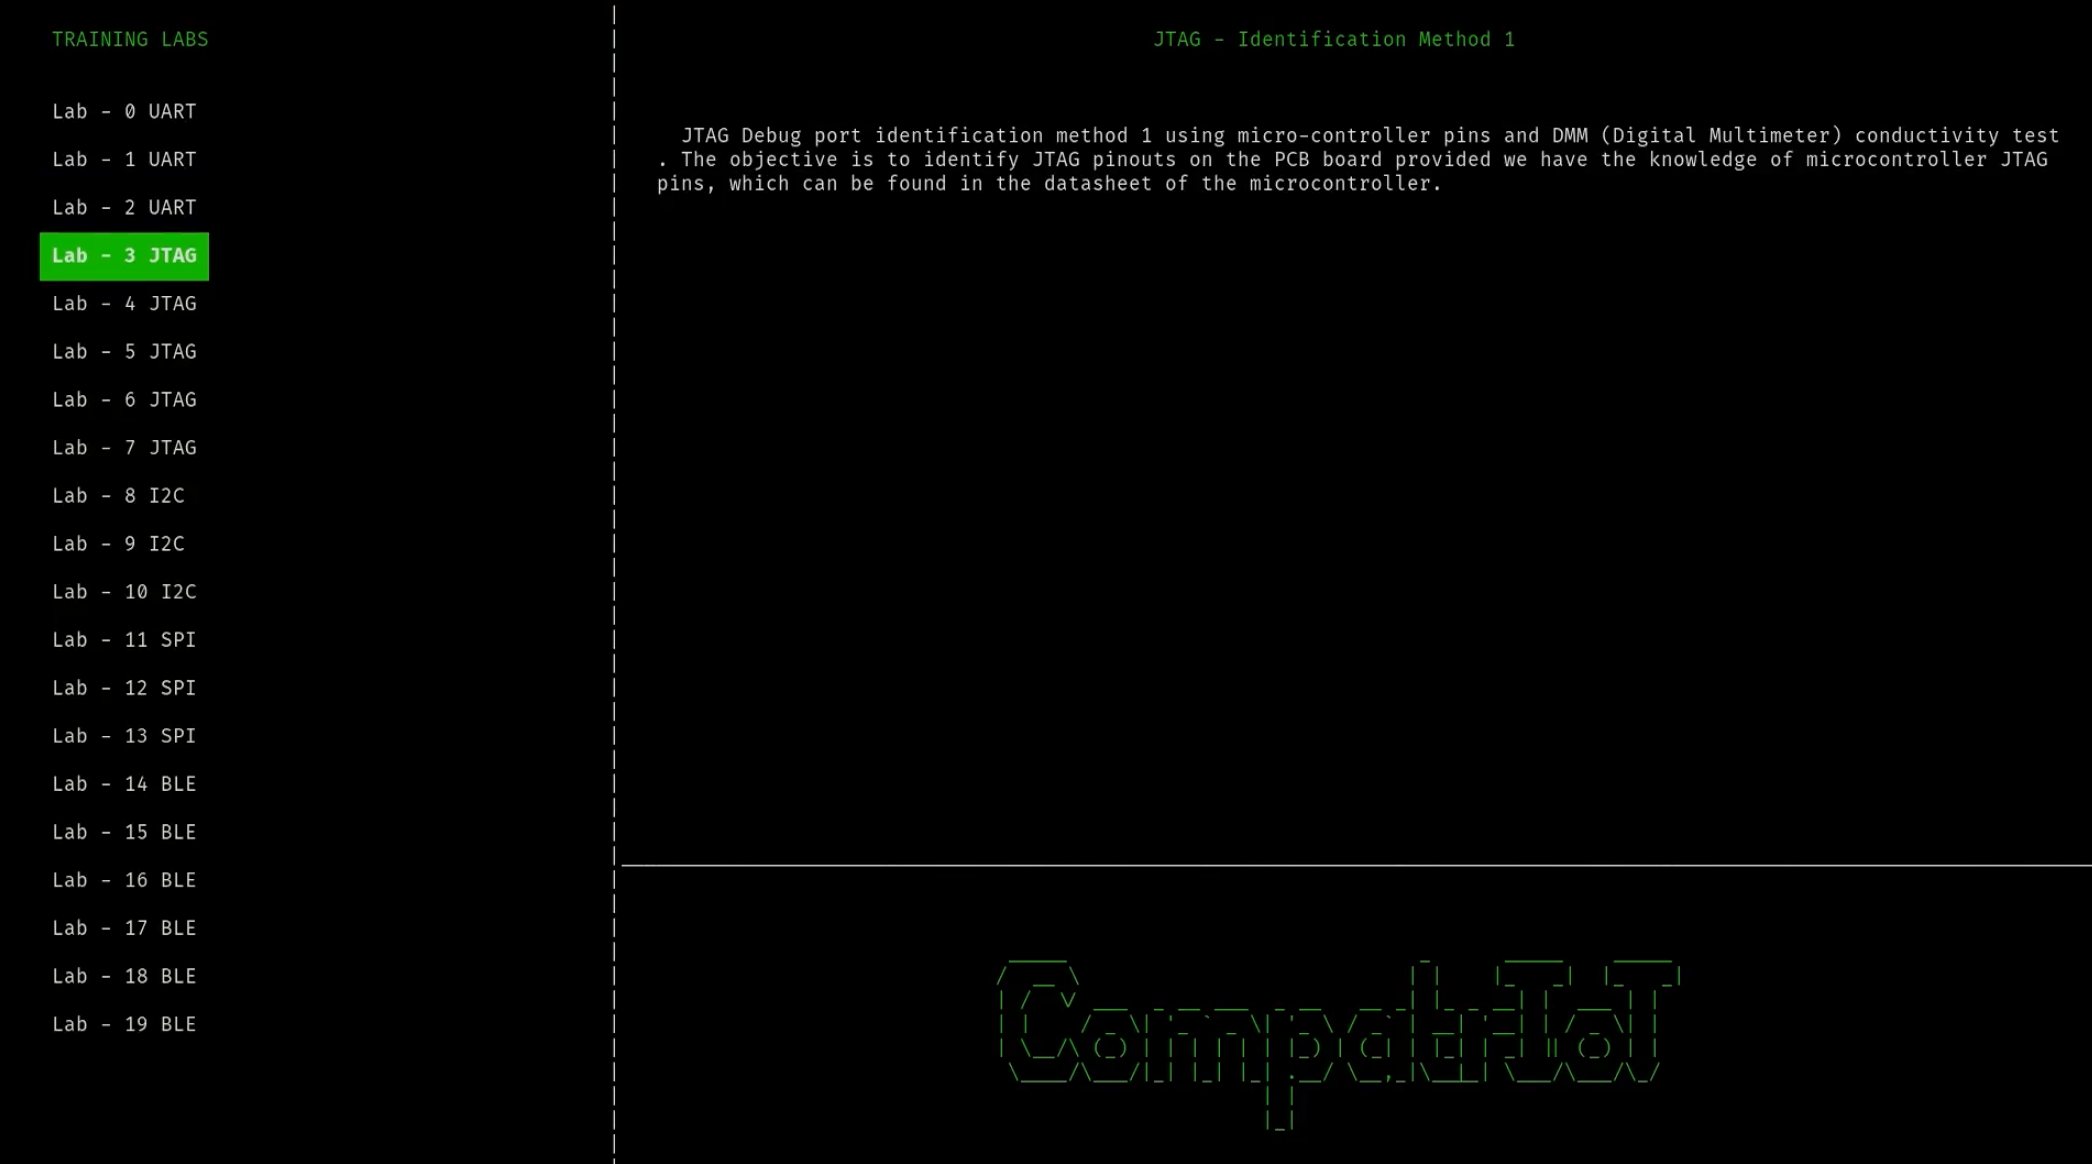
The lab console — a terminal-native interface that walks you through each challenge.
Why it matters
Everything is open — hardware designs, firmware, and documentation — so anyone can build, extend, or teach with it. It compresses what usually takes a shelf of dev boards and scattered CTF challenges into one board with a structured learning path: real protocols, real extraction, real exploitation, from beginner to advanced.